SAST tools scan source code for security flaws before the app runs. Top picks: Aikido Security for an all-in-one platform with a free plan, Semgrep and SonarQube Community Build for open source, Snyk Code for a free IDE-first start, and Veracode, Checkmarx and Fortify for quote-only enterprise buys.
SAST (static application security testing) scanning tools read your source code and flag vulnerabilities such as SQL injection and buffer overflows without running the app. DAST tools work the other way. They test a running application as a black box.
Prices in the table and in the sections below come from each vendor's pricing or product page as of October 2026. If you want free options, check the free column or jump to open-source SAST tools.
| Tool | Best for | Free option | Paid price |
|---|---|---|---|
| Aikido Security | SAST, SCA, IaC and DAST in one tool | Developer plan: 2 users, 10 repos | Basic $350/month incl. 10 users |
| Semgrep | Open-source engine | Free for up to 10 contributors | Teams from $30/month per contributor |
| SonarQube | Code quality plus security | Community Build, Cloud Free up to 50k LOC | Cloud Team from $34/month, Server by LOC |
| Snyk Code | SAST in the IDE | 100 Snyk Code tests/month | Team from $25/month |
| Checkmarx | Large enterprises | None listed | Quote only |
| Veracode | Enterprise buyers | None listed | Quote only |
| Fortify | Hosted or on-prem enterprise scanning | None listed | No public price |
| Codacy | Quality and security checks together | Free for open-source projects | Team from $18/dev/month, billed yearly |
| GitLab SAST | Teams on GitLab | Basic SAST in the Free tier | Advanced SAST needs Ultimate, custom price |
| GitHub Advanced Security | Teams on GitHub | Code scanning on by default for public repos | Code Security $30 per active committer/month |
Klocwork, for C and C++ teams, is covered after the ten.
Aikido Security
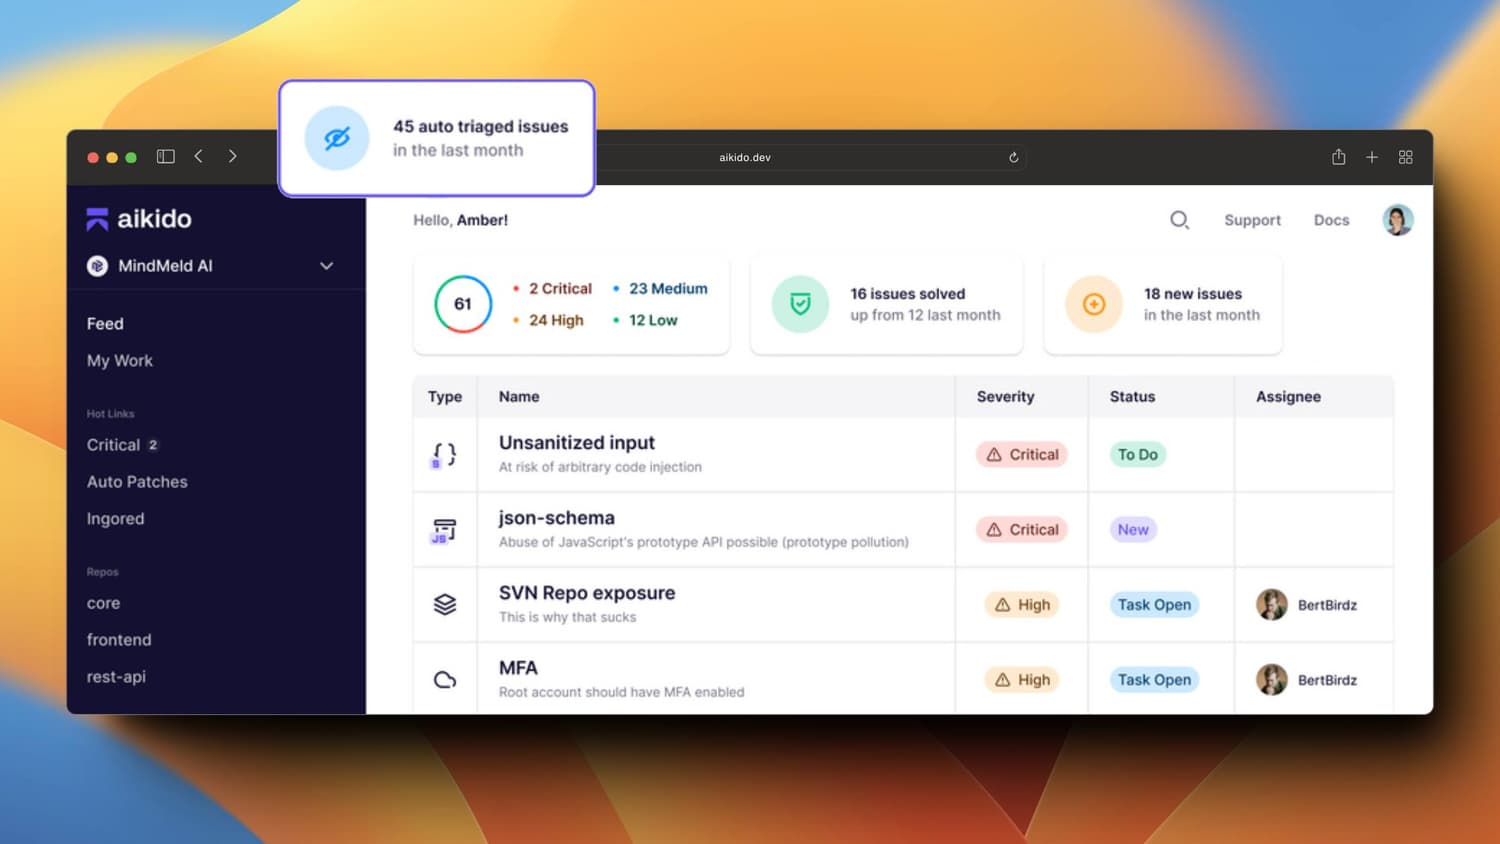
Aikido Security is an application security platform. It puts SAST, dependency scanning (SCA), secrets, infrastructure as code (IaC), containers and DAST in one dashboard, and it connects to GitHub, GitLab, Bitbucket and Azure DevOps.
- Aikido says it triages unreachable vulnerabilities and uses AI-powered triaging to filter out non-security alerts, per its SAST page.
- AI AutoFix suggests code fixes for certain vulnerabilities. The free plan includes 10 a month.
- The Basic plan syncs issues to Jira and Linear and compliance data to Drata and Vanta (see Drata alternatives).
Pricing: The Developer plan is free: 2 users, 10 repos, 2 container images, 1 domain and 1 cloud account. It includes SAST and AI SAST, SCA, secrets, IaC, DAST and IDE plugins. Basic is $350/month for 10 users (100 repos, plus PR code quality checks). Pro is $700/month for 10 users and has 200 repos, on-prem scanning, malware detection and same-day support. Advanced is $1,050/month for 10 users and has 500 repos, FIPS base images and priority support. Aikido shows prices in your local currency, so in euros these read EUR 300, 600 and 900. Annual billing is 10% off, and Enterprise is custom. See Aikido pricing.
Best for teams that want SAST, SCA, secrets, IaC and DAST in one tool and a free start. Skip if you have more than 2 users and want it free, because paid plans start at $350/month for 10 users.
Semgrep
Semgrep is a static analysis engine, open source under the LGPL-2.1 license, with a hosted product built on it. According to the project README, Semgrep Code supports 30+ languages.
- The free Edition covers up to 10 contributors and 10 repos. Teams starts at $30/month per contributor for Code or Supply Chain, and Secrets is $15 (pricing).
- The open-source Community Edition "can only analyze interactions within a single function," per the Semgrep docs. By default, Semgrep Code analyzes beyond a single function but within a single file, and it supports cross-file analysis.
Best for open-source use, since the engine is LGPL-2.1 and the free Edition covers up to 10 contributors. Skip if you need cross-function analysis from the open-source engine alone.
SonarQube
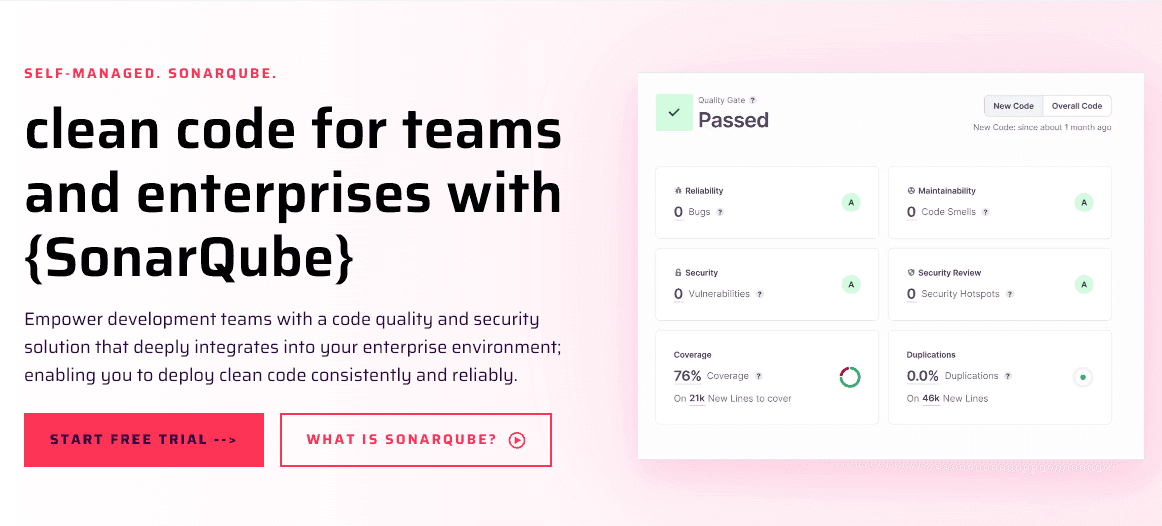
SonarQube checks code quality and security. The free, open-source edition is SonarQube Community Build, and the source is on GitHub. The paid Server editions are Developer, Enterprise and Data Center.
- Community Build supports 22 languages and frameworks, per the downloads page.
- It works with GitHub, GitLab, Azure and Bitbucket, in the cloud or on-prem, and runs on Docker or Kubernetes.
- The quality gate fails a pipeline when code misses your standards, so it can't be merged or deployed.
Pricing: SonarQube Cloud Free covers private projects up to 50k lines of code (LOC). Cloud Team starts at $34/month for up to 100k LOC (an FAQ on the same page says $32). Enterprise is custom. The Server Developer and Enterprise editions are priced per instance per year by LOC, and Sonar publishes no list price. See Sonar pricing.
Best for teams that want code quality and security checks together and a free, self-hosted start. Skip if you want a Server list price, because Sonar quotes it by LOC.
Snyk
Snyk Code is Snyk's SAST product. It scans in your IDE and shows suggested fixes next to your source code.
- Real-time results with automatic scanning in your code editor, plus fix advice for potential vulnerabilities.
- It prioritizes the top code risks by looking at the context of the vulnerability.
Pricing: Free is $0 with 100 Snyk Code (SAST) tests/month and 5 projects. Team starts at $25/month for development teams of up to 10 developers, with 1,000 Snyk Code tests/month and 100 projects. Enterprise is credit-based and sold through sales. See Snyk plans.
Best for small teams that want to try SAST in the IDE for free. Skip the free plan if you run more than 100 Snyk Code tests a month.
Checkmarx
Checkmarx SAST is part of the Checkmarx One platform and is built for enterprises.
- Checkmarx says it pairs a deterministic engine for core languages with an AI-powered engine for the rest.
- It scans directly from GitHub, GitLab, Azure and Bitbucket, with no compilation.
Pricing: Quote only. Checkmarx lists packages (Essentials, Professional, Enterprise, Start with SAST and Start with Supply Chain) and says pricing is tailored to your environment. See Checkmarx pricing or request a demo.
Best for large teams that buy through a sales process. Skip if you want a published price.
Veracode
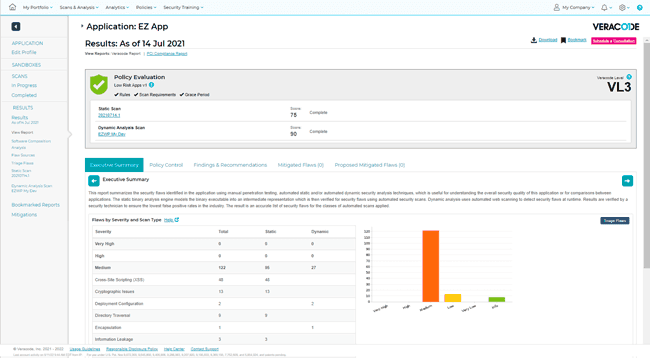
Veracode Static Analysis (SAST) gives developers real-time feedback in the IDE and plugs into CI/CD pipelines.
- Supports over 100 languages and frameworks.
- Gives real-time feedback in your IDE so developers fix flaws sooner.
- Integrates with IDEs, CI/CD pipelines and the command line.
Pricing: Quote only. The product page offers a demo request and a datasheet download, and no price.
Best for enterprise buyers who want a vendor-led rollout. Skip if you want to start without talking to sales.
Fortify
Fortify SAST by OpenText is a static code analyzer. The wider Fortify platform adds SCA and DAST.
- The product page says 44+ languages and 350+ frameworks. Its FAQ says 33+ programming languages.
- It runs as Fortify on Demand (SaaS), a private hosted option or an off-cloud install.
- It scans infrastructure as code for Docker, Kubernetes and serverless.
- Static analysis extends to REST APIs.
Pricing: No price is published.
Best for enterprises that want hosted or on-prem scanning from one vendor. Skip if you need a price before a sales call.
Codacy
Codacy covers code quality and security. Codacy Quality enforces coding standards and uses AI to suggest fixes. Codacy Security adds SAST, SCA and secrets scanning on the Developer and Team plans, and its pricing page lists DAST and container scanning on Business.
- SAST detects security violations such as hardcoded secrets, broken access control and injection threats like SQL injection.
- SCA monitors open-source libraries for known vulnerabilities and CVEs, and secrets scanning checks code for exposed API keys and passwords.
Pricing: Developer is $0 for individual developers. Team starts at $18 per developer/month billed yearly ($21 billed monthly) for up to 30 developers, and it is free forever for open-source projects. Business is custom. See Codacy pricing.
Best for small teams that want quality and security checks together, and open-source projects. Skip if you have more than 30 developers, because Team stops there and Business is custom.
GitLab
GitLab SAST checks your source code for known vulnerabilities inside GitLab CI/CD. Free, Premium and Ultimate all get basic scanning with open-source analyzers, and the reports download as JSON job artifacts. GitLab Advanced SAST, which scans across files, is Ultimate only. With Ultimate you can also use the results in approval workflows or review them in the security dashboard.
- The docs list 21 languages. Named analyzers include the Semgrep-based analyzer, GitLab Advanced SAST, PMD-Apex, Sobelow, SpotBugs, Kubesec and clangsa.
- GitLab Duo false positive detection analyzes critical and high findings. It needs Ultimate plus the GitLab Duo add-on.
Pricing: Free and Premium include basic scans. Premium is $29 per user/month billed annually. Ultimate has no public price, and GitLab says its enterprise-grade scanning and management features are Ultimate only. See GitLab pricing.
Best for teams already on GitLab CI/CD that want basic SAST in any tier. Skip if you need Advanced SAST without Ultimate.
GitHub Advanced Security
CodeQL is the analysis engine behind GitHub Advanced Security. It contains libraries and queries, and security researchers and developers use it to automate security checks and run variant analysis. Code scanning runs CodeQL or a third-party tool. GitHub now sells Advanced Security as two products, GitHub Code Security and GitHub Secret Protection.
- CodeQL has extensive documentation, a library of queries by GitHub researchers and community contributors, and support for writing your own queries.
- Copilot Autofix, part of GitHub Code Security, generates fixes for code scanning alerts.
Pricing: Code scanning is enabled by default for public repositories. To buy GitHub Code Security or GitHub Secret Protection you must be on a GitHub Team or GitHub Enterprise plan. Code Security is $30 and Secret Protection is $19, both per active committer/month. See GitHub Advanced Security.
Best for teams already on GitHub Team or Enterprise. Skip if you are on neither plan, because you can't buy either product.
Klocwork
Klocwork is a bonus pick for C and C++ teams. Perforce lists it for C, C++, C#, Rust, Java, JavaScript, Python and Kotlin, with coverage of CWE, OWASP, CERT, PCI DSS, DISA STIG and ISO/IEC TS 17961.
Pricing: Quote only. The Klocwork page offers a free trial request and a contact link.
Open-source SAST tools
These four have a free, open-source edition or engine.
- Semgrep Community Edition is LGPL-2.1 and analyzes a single function at a time.
- SonarQube Community Build is free and open source, with 22 languages and frameworks.
- Bandit is Apache-2.0 and finds common security issues in Python code.
- gosec is Apache-2.0 and is a Go security checker.
Which one to pick
- Small team, free start: Aikido's Developer plan or Snyk Free.
- An open-source engine you run yourself: Semgrep or SonarQube Community Build, or Bandit for Python and gosec for Go.
- Already on GitHub Team or Enterprise: GitHub Code Security at $30 per active committer/month.
- On GitLab Ultimate: GitLab Advanced SAST.
- Large enterprise with a procurement process: Veracode, Checkmarx or Fortify. None lists a price.
- C or C++ code: Klocwork, quote only.
To try one, start free with Aikido.